The NJCCIC received incident reports detailing the latest tactic in a long series of scams involving the New Jersey Motor Vehicle Commission (NJMVC). In this campaign, threat actors use search engine optimization (SEO) poisoning, a cyberattack that manipulates search engine rankings to push malicious websites to the top of search results.
Incident reports indicated that when searching for the NJMVC portal to renew a vehicle registration, selecting the first result led to amvsonline[.]com (American Motor Vehicle Services), a convincing replica of the official NJMVC website. The malicious website prompted for a license plate number, located the correct vehicle records, and auto-populated personal identification—including full name and home address.
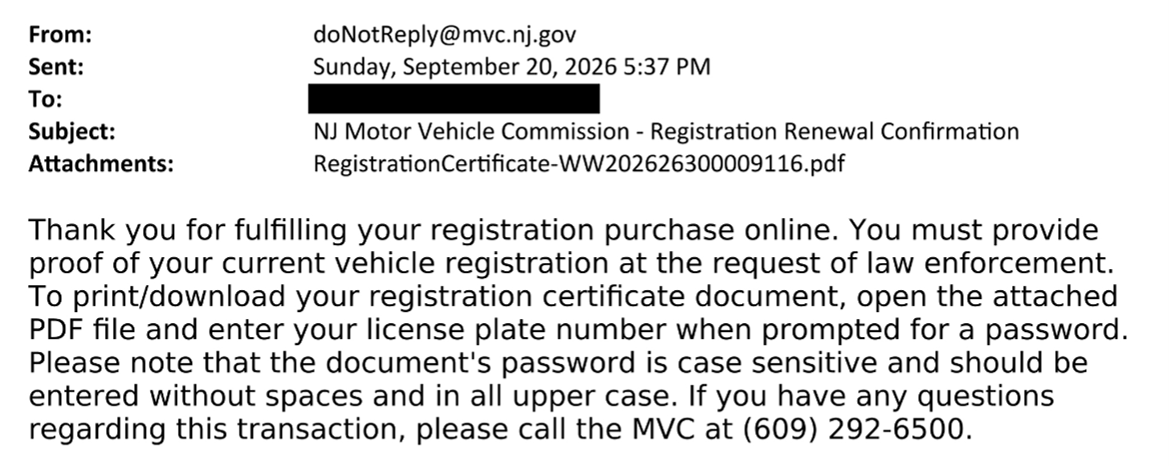
Reports indicated that after entering credit card information to complete the renewal payment, the site displayed an error message reading, "Card could not be used." An email from the spoofed donotreply[@]mvc[.]nj[.]gov confirmed the renewal and included a password-protected Adobe PDF registration document that required the target’s license plate number to open.
Recommendations
- Exercise caution when utilizing search engines; threat actors strategically use SEO poisoning to cause malicious websites to appear at the top of search engine result pages.
- Type official website URLs into browsers manually and only submit account credentials or sensitive information on official websites.
- Users who submitted payment information to these webpages are advised to contact their banking institutions to report the fraudulent purchases.